SOC 2 Compliance Software Development Company
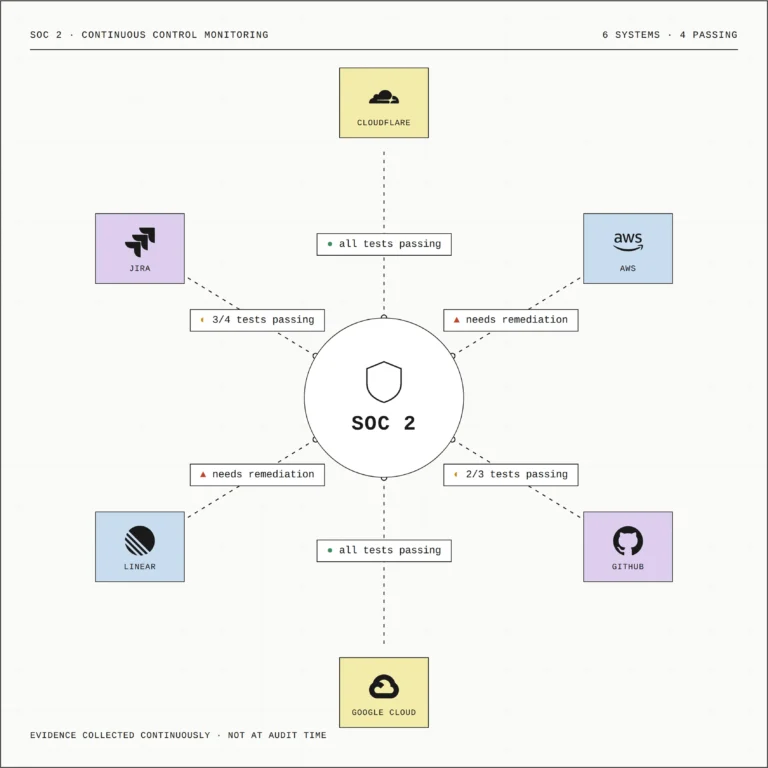
We build the software controls a SOC 2 audit actually samples: audit events that name the human behind an impersonated session, production access that expires on its own, and evidence your team can re-run as a query. SOC 2 is an attestation of what your systems did across an observation period, which is why the engineering has to be right before that period starts.
Trusted by teams at:


Teamvoy has delivered engineering work for 150+ companies.
Verified B2B client reviews from fintech, insurance, healthcare, and hi-tech engagements.
A B2B review platform that connects businesses with verified software solutions providers.
Transparent platform where current and former employees share company reviews and interview experiences.
What Our Clients Say
Teamvoy has successfully launched the system within the set timeline and integrated all the required tools and features. The collaborative team led regular meetings, delivered on time, and communicated effectively. Their proactive problem-solving approach and commitment to innovation stand out.
Jim Hill, Director of Marketing & Business Development, Market Access Direct, LLC
Teamvoy’s support and expertise have been integral in helping the client build and scale their product. An agile partner, they manage their tasks well and are consistent in delivering according to schedule. Their strong understanding of blockchain and the quality of their work make them stand out
Gordon Little, Managing Director, Iress
One privileged access, seven layers
A support engineer opening one customer record looks like a single click. It is seven handovers, and an auditor sampling that period will touch every one of them.
01. Identity and session
The engineer arrives through your identity provider. A SAML or OIDC assertion, a second factor, group claims, and a session token with a lifetime.
Breaks when: the group is revoked in the identity provider but the claim is cached in the session, so a removed engineer keeps access until the token expires.
03. Elevation and break-glass
Production access is granted just in time, against a ticket, with an expiry and a reason.
Breaks when: the grant has no expiry. A one-off elevation quietly becomes a standing admin role, and every sample pulled from that period carries it.
04. Data path and keys
The service decrypts only what it needs, keys come from the key manager, and sensitive fields stay masked inside support tooling.
Breaks when: keys are rotated for the live database but not for the backups, so the restore path runs on a key that never entered the rotation record.
05. Audit event
The action is written as an immutable event: actor, resource, action, timestamp, reason.
Breaks when: the event records the service account rather than the person behind the impersonated session, and every record in the sample resolves to the same identity.
06. Retention and integrity
Events ship to append-only storage, with a retention window that covers the whole observation period and evidence that nothing was edited.
Breaks when: the audit stream inherits the retention set for debug logs, and the evidence from the opening months of the period has already aged out.
07. Evidence extraction
What happens:
The trace closes at 380 ms. Crash-free session, journey funnel step, latency budget, cost per call – and the link from a one-star review back to this exact request.
What fails:
Telemetry that stops at the client. You know the app crashed; you cannot tell which service call caused it, so the rating never moves.
What can change:
Tooling. OpenTelemetry means the collector or the backend can change without re-instrumenting a line of application code.
SOC 2 Compliance Engineering Success Stories

How AI Agent Reworked Integration Delivery From the Ground Up
Data Migration in Insurance: Moving Data Safely
Hybrid Cloud Banking Architecture: Zero Downtime, ~400K Users, Seven Banks
SOC 2 Compliance Engineering Services We Offer
Six offerings, each scoped separately against the controls your auditor will sample rather than against the full criteria list.
Audit Logging and Evidence Pipelines
An append-only event on every privileged path, carrying the human actor even when the session is impersonated. Each control ships with the export query that answers a sample request, checked into the repository next to the code it proves.
Access Control and Provisioning
Authorization decided at the API with tenant scope in the query itself, not in the screen that hides the button. Production elevation is granted against a ticket and expires without anyone remembering to revoke it.
Secure SDLC and Change Management
Branch protection, review gates and pipeline scanning arranged so the change record is a by-product of shipping rather than a monthly reconstruction. Every deployment traces back to the ticket and the approval that released it.
Cloud Infrastructure Hardening
Terraform baselines that make the hardened configuration the default rather than a checklist someone applies after the fact. Key rotation covers the restore path, so backups are not encrypted under a key that never entered the rotation record.
Monitoring and Incident Evidence
Alerting wired so the Availability criterion is answered by your existing monitoring rather than by a screenshot. Incident timelines, on-call handovers and postmortems are captured as they happen and mapped to the control they satisfy.
Customer-Facing Security Features
The features that appear in enterprise security questionnaires and then stall the deal: tenant SSO, an audit log your customer can export, retention and deletion they can configure. Built as product surface, so your buyers answer their own questions.
Why choose Teamvoy for SOC 2 compliance engineering?
Four positions we hold on every SOC 2 engagement, including the two that cost us work.
Adopt Modern Technologies
Tech stack modernization replaces outdated and unsupported tools with current ones that adhere to today’s standards.
Reduce Maintenance Costs
By moving away from legacy technologies that require constant repairs and specialized skills, your maintenance costs may decrease by 20–40%, depending on your system size.
Enable Smooth Scaling
With cloud-native tools and containerization, your products can grow as your business grows.
Prepare A Base For Innovation
An outdated codebase slows progress. After legacy software modernization, you can integrate AI, blockchain, IoT, and other emerging technologies.
Not sure which of your controls would
survive a sample request?
Three ways to start
Pick the smallest one that answers your question. None of them require a procurement cycle.
SOC 2 Readiness Review
We map your systems against the Trust Services Criteria and hand back a control-by-control gap register: what needs code, what needs a policy, what your compliance platform already covers. Yours to take to any vendor or auditor, including ones that are not us.
One Control Path in Your Environment
We instrument a single privileged path in your own repositories and cloud accounts: the audit event, the actor identity behind impersonation, the retention, and the export query your auditor can sample. You see how we work before the scope grows.
Fifteen Minutes with a CTO
Tell us your audit date and where the gaps sit. If the work belongs to your compliance platform, your operations lead or your auditor rather than to engineering, we will say so on the call and there is nothing further to discuss.
We engineer for:
Bring us the control with no evidence behind it.
Talk to a Chief Technology Officer on the first call.